'Kisses from Prague': The fall of a Russian ransomware giant / Photo: © NATIONAL CRIME AGENCY/AFP/File

The sudden fall of a ransomware supplier once described as the world's most harmful cybercrime group has raised questions about Moscow's role in its development and the fate of its founder.
LockBit supplied ransomware to a global network of hackers, who used the services in recent years to attacks thousands of targets worldwide and rake in tens of millions of dollars.
Ransomware is a type of malicious software, or malware, that steals data and prevents a user from accessing computer files or networks until a ransom is paid for their return.
LockBit supplied a worldwide network of hackers with the tools and infrastructure to carry out attacks, communicate with victims, store the stolen information and launder cryptocurrencies.
According to the US State Department, between 2020 and early 2024 LockBit ransomware carried out attacks on more than 2,500 victims around the world.
It issued ransom demands worth hundreds of millions of dollars and received at least $150 million in actual ransom payments made in the form of digital currency.
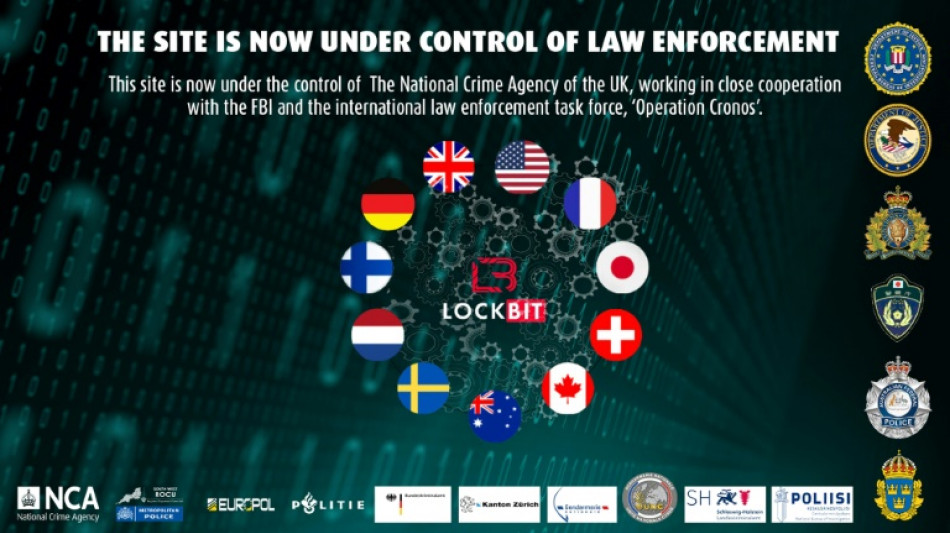
But LockBit was dealt its first devastating blow in February 2024 when the British National Crime Agency (NCA), working with the US FBI and several other nations, announced it had infiltrated the group's network and took control of its services.
Later that year, the NCA announced it had identified LockBit's leader as a Russian named Dmitry Khoroshev (alias LockBitSupp).
The US State Department said it was offering a reward of up to $10 million for information leading to his arrest.
Lockbit, which the NCA said was "once the world's most harmful cybercrime group", sought to adapt by using different sites.
But earlier this year it suffered an even more devastating breach and received a taste of its own medicine.
Its systems were hacked and some of its data stolen in an attack whose origins were mysterious and has, unusually in the cybercrime world, never been claimed.
"Don't do crime. Crime is bad. Xoxo from Prague," said a cryptic message written on the website it had been using.
- 'Others grow back' -
"Lockbit was number one. It was in survival mode and took another hit" with the leak, said Vincent Hinderer, Cyber Threat Intelligence team manager with Orange Cyberdefense.
"Not all members of the group have been arrested. Other, less experienced cybercriminals may join," he added.
However, observations of online chats, negotiations and virtual currency wallets indicate "attacks with small ransoms, and therefore a relatively low return on investment", he said.
A French cyberdefence official, who asked not to be named, said the fall of LockBit in no way represented the end of cybercrime.
"You can draw a parallel with counterterrorism. You cut off one head and others grow back."
The balance of power also shifts fast.
Other groups are replacing LockBit, which analysts said was responsible in 2023 for 44 percent of ransomware attacks worldwide.
"Some groups achieve a dominant position and then fall into disuse because they quit on their own, are challenged or there's a breakdown in trust that causes them to lose their partners," said Hinderer.
"Conti was the leader, then LockBit, then RansomHub. Today, other groups are regaining leadership. Groups that were in the top five or top 10 are rising, while others are falling."
In a strange twist, the LockBit data leak revealed that one of its affiliates had attacked a Russian town of 50,000 inhabitants.
LockBit immediately offered the town decryption software -- an antidote to the poison.
But it did not work, the French official told AFP.
"It was reported to the FSB (security service), who quietly resolved the problem," the official said.
- 'Complicit' -
One thing appears to be clear -- the field is dominated by the Russian-speaking world.
Among the top 10 cybercrime service providers, "there are two Chinese groups", said a senior executive working on cybercrime in the private sector.
"All the others are Russian-speaking, most of them still physically located in Russia or its satellites," said the executive, who also requested anonymity.
It is harder to ascertain what role the Russian state might play -- a question all the more pertinent since Moscow's 2022 invasion of Ukraine.
"We can't say that the groups are sponsored by the Russian state but the impunity they enjoy are enough to make it complicit," argued the French official, pointing to a "porosity" between the groups and the security services.
The whereabouts and status of Khoroshev are also a mystery.
The bounty notice from the US State Department, which said Khoroshev was aged 32, gives his date of birth and passport number but says his height, weight and eye colour are unknown.
His wanted picture shows an intense man with cropped hair and bulging muscular forearms.
"As long as he doesn't leave Russia, he won't be arrested," said the private sector expert. "(But) we're not sure he's alive."
"The Russian state lets the groups do what they want. It's very happy with this form of continuous harassment," he alleged.
In the past, there was some cooperation between Washington and Moscow over cybercrime but all this changed with the Russian invasion of Ukraine.
French expert Damien Bancal cites the case of Sodinokibi, a hacker group also known as REvil, which was dismantled in January 2022.
"The FBI helped the FSB arrest the group. During the arrests, they found gold bars and their mattresses were stuffed with cash," he said.
But since the invasion of Ukraine, "no-one is cooperating with anyone any more".
Asked if the US has questioned Moscow about Khoroshev after the bounty was placed on his head, Kremlin spokesman Dmitry Peskov said: "Unfortunately, I have no information."
X.So--ThChM